

Quick Answer: Chick-fil-A has told customers that unauthorized parties broke into some Chick-fil-A One loyalty accounts between June 17 and June 19, 2026. This was not a hack of Chick-fil-A’s own systems — attackers used usernames and passwords stolen from other companies’ past breaches and simply tried them here, a tactic called credential stuffing. If you have a Chick-fil-A One account, do three things today: change its password to something unique, remove any saved payment card, and turn on two-step verification if it’s offered. The real lesson costs nothing and protects far more than your chicken money: stop reusing passwords.
Expert Context: I’ve spent 30 years documenting how financial predators operate, and the single most common thread I see isn’t sophisticated hacking — it’s one reused password quietly turning into access to everything. I’ve watched a leaked login from some forgotten website become the doorway to someone’s bank, their credit accounts, and their savings. This Chick-fil-A story is small on its own. The habit behind it is what empties accounts.
The headline says “Chick-fil-A data breach,” but that framing hides the part that actually matters to you: the passwords weren’t stolen from Chick-fil-A. They were stolen from somewhere else — an old retailer, a hacked forum, a breach you forgot about years ago — and then run against Chick-fil-A’s login page by an automated program hoping you reused the same password. For thousands of people, the bet paid off.
Key Terms Defined
Credential stuffing: An automated attack where criminals take username-and-password pairs leaked in previous breaches and rapidly “stuff” them into other websites’ login forms, betting that people reuse the same password across accounts. The company being logged into wasn’t hacked — you were, somewhere else, earlier.
Data breach vs. account takeover: A breach is when a company’s own systems are penetrated. An account takeover is when someone logs into your account using credentials they got elsewhere. This incident is the second kind, which is why the fix lives largely with you, not just with the company.
What was actually exposed
According to Chick-fil-A’s notifications, the accessed loyalty accounts could have exposed your name, email address, Chick-fil-A One membership number, mobile pay number, QR code, the last four digits of a credit or debit card, and the amount of Chick-fil-A credit stored on the account. If you had saved them, the exposed data may also have included the month and day of your birthday, your phone number, and your address. Chick-fil-A reported roughly 2,182 affected customers to the Texas Attorney General and sent notices to customers across about ten states, according to CBS News reporting. The company says it forced logouts of affected accounts and removed stored payment methods.
None of that is catastrophic by itself. But two pieces matter more than they look: the stored account credit is real money someone could spend, and the combination of your birthday, phone, and address is exactly the kind of detail scammers stitch together to impersonate you elsewhere. A last-four card number plus your name and email is enough to make a phishing text feel legitimate.
Why this is really a password-reuse story
The Claim: “Chick-fil-A got hacked, so there was nothing I could have done — and nothing I can do now.”
The Reality: The attackers didn’t crack Chick-fil-A. As security researchers at Malwarebytes documented, they logged in with passwords harvested from unrelated, earlier breaches. That means the accounts that fell were overwhelmingly the ones using a password that had already leaked somewhere else. The flip side is the good news: a unique password on this account would have made you nearly untouchable to this attack — and it still will on every other account you own.
The 3 moves to make today
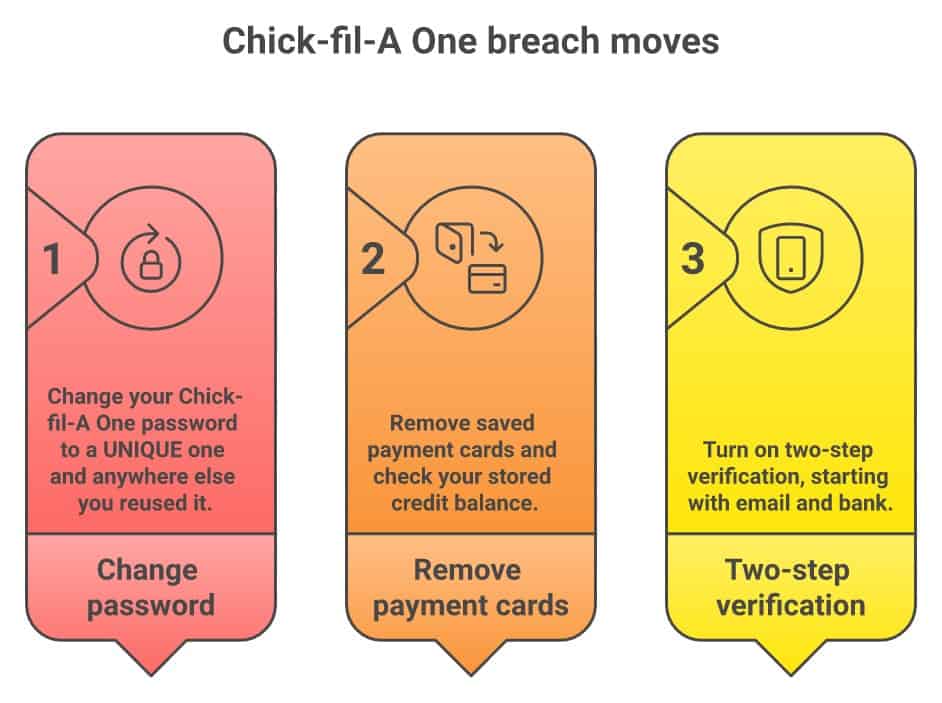
- Change your Chick-fil-A One password to a unique one. Not a variation of your usual password — a genuinely different one. If you used that same password anywhere else (email, bank, Amazon), change it there too, starting with anything tied to money.
- Remove saved payment cards and check your stored credit. Delete cards saved in the app, and note your Chick-fil-A credit balance in case you need to dispute a spend. Watch the card whose last four digits were exposed for anything odd.
- Turn on two-step verification wherever it’s offered. Even if a criminal has your password, a second step usually stops them cold — and an authenticator app is stronger than a text-message code, which can be intercepted. Prioritize your email and bank accounts; those are the keys to everything else.
- Can’t keep unique passwords straight? Use a password manager. A reputable one (Bitwarden, 1Password, or the manager built into your browser or phone) creates and remembers a different strong password for every account, so a leak at one site can’t unlock the rest.
Expect the follow-up scam. After a breach makes the news, fraudsters send texts and emails posing as the company — “Your Chick-fil-A account was compromised, click here to secure it.” That link is the actual attack. Never click a link in a breach notice; open the app or type the address yourself. And check whether your email has turned up in known breaches at the free, reputable site Have I Been Pwned. If a message pressures you to act in the next few minutes, that urgency is the tell.
Why a chicken app matters to your financial life
You might reasonably think a fast-food rewards account isn’t worth this much attention. Here’s why I’m spending it: the exact same automated attack that hit these loyalty accounts is run, every single day, against banking logins, credit card portals, and retirement accounts. The only thing standing between a years-old leaked password and your real money is whether you reused it. A breach at a restaurant is a cheap, harmless reminder to fix a habit before it costs you something that isn’t harmless at all.
Key Takeaways
- This was credential stuffing, not a hack of Chick-fil-A’s systems — reused passwords are what let attackers in.
- Exposed data could include name, contact info, last-4 of a card, QR code, and stored account credit.
- Three free moves today: unique password, remove saved cards, turn on two-step verification.
- Never click a link inside a breach notice — that’s how the follow-up scam gets you.
- The habit you fix here protects your bank, credit, and retirement accounts too.
The Bottom Line
If you’ve been using the same password across accounts for years — like most people quietly do — this is your low-cost wake-up call, and I’d rather you get it from a chicken app than from your bank. You didn’t do anything shameful; password reuse is human, and the companies that let it happen share the blame. But the fix is entirely in your hands and it’s free: one unique password at a time, starting with the accounts that hold your money. Take twenty minutes today, and you’ll have quietly closed a door that criminals are rattling on millions of us right now. Then send this to someone you love who still uses “the one password they always use.”
Frequently Asked Questions
Was Chick-fil-A itself hacked?
No. Chick-fil-A says its own systems were not breached. Attackers used usernames and passwords stolen from other companies’ past breaches and tried them against Chick-fil-A One accounts — an attack called credential stuffing that succeeds only when people reuse passwords.
The Daily Money Brief — Free, at 10 AM
Money you may be owed, scams to dodge, and the fine print decoded — the consumer money news that affects your wallet, every weekday.
What information was exposed?
Potentially your name, email, Chick-fil-A One membership and mobile pay numbers, QR code, the last four digits of a card, and your stored Chick-fil-A credit — plus, if you saved them, your birthday (month and day), phone number, and address.
What should I do right now?
Change your Chick-fil-A One password to a unique one, remove saved payment cards, and enable two-step verification. If you reused that password elsewhere — especially on financial accounts — change it there too.
Is my money at risk?
Directly, the exposure is limited to stored Chick-fil-A credit and the last four digits of a card. The bigger risk is indirect: if the same password unlocks your bank or email, that’s where real damage happens. Fixing password reuse is the actual protection.
How do I know if my info was part of this or other breaches?
If you were affected, Chick-fil-A notified you directly. To check whether your email has appeared in known breaches generally, use the free, reputable service Have I Been Pwned, and never trust a link sent inside an unsolicited “breach alert” message.
This is what I’m seeing after 30 years of watching how a single exposed detail becomes the opening for financial fraud — take it as one informed perspective, not marching orders. Only you know your full situation, and nobody gets to tell you what to do with your money. Not me, not anyone. Use this as input for your own decision.
Dealing With Debt? Understanding your options is the first step. See how all your debt relief options compare — including ones most sites won’t tell you about. The Find Your Path quiz gives a recommendation based on your actual numbers, and the Scam-O-Meter checks any company’s complaint history before you sign. Federal Reserve Bank of New York research shows bankruptcy filers recover faster than those who don’t file.



